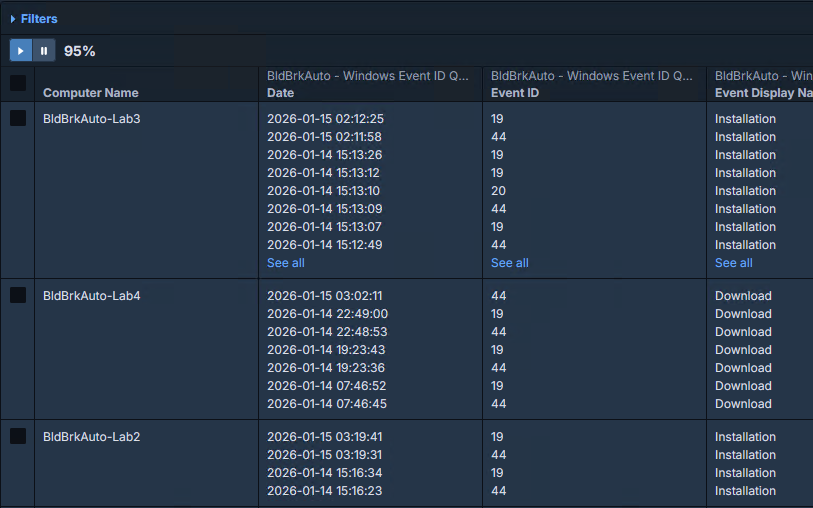
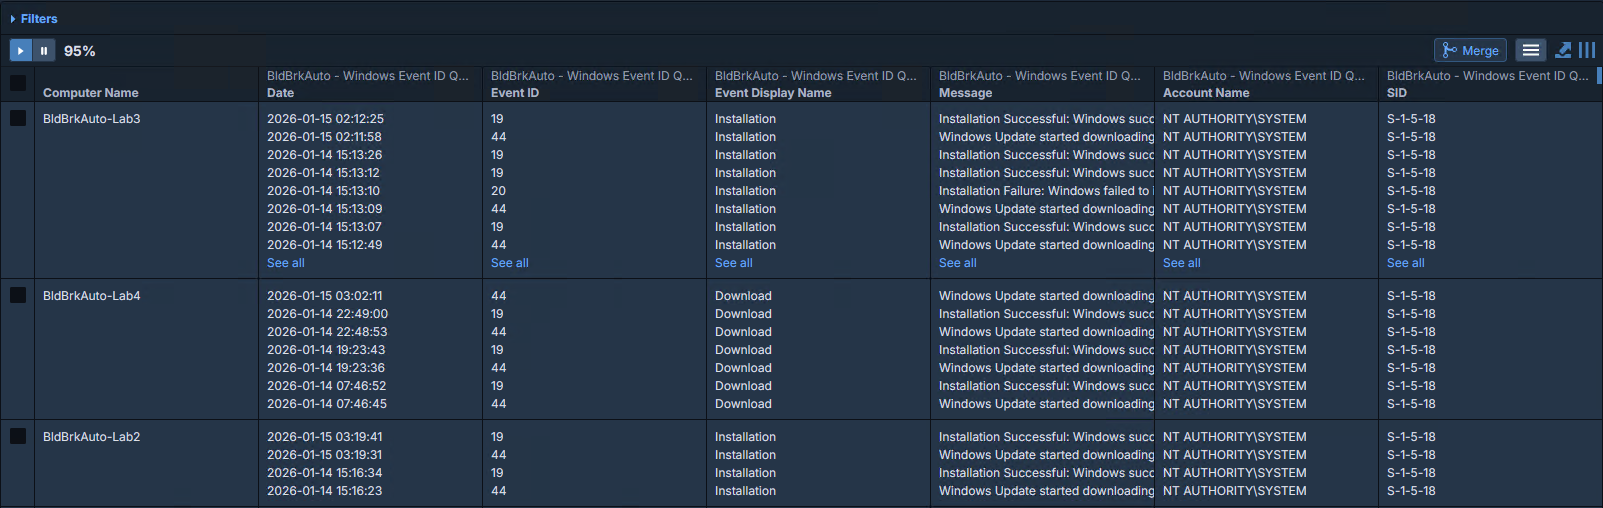
Windows event logs are a goldmine of diagnostic data and a chore to use at scale unless you have already paid for a log aggregator. This is a parameterised sensor: name the log, the event IDs and the window, and every endpoint returns the matching records as structured columns you can question, filter and merge like any other Tanium data. SIDs are resolved to account names on the endpoint, so the output reads without a second lookup. It came out of a client issue that needed more event log sleuthing than was reasonable by hand.
Read the full write-up: Investigating Windows Events at Scale